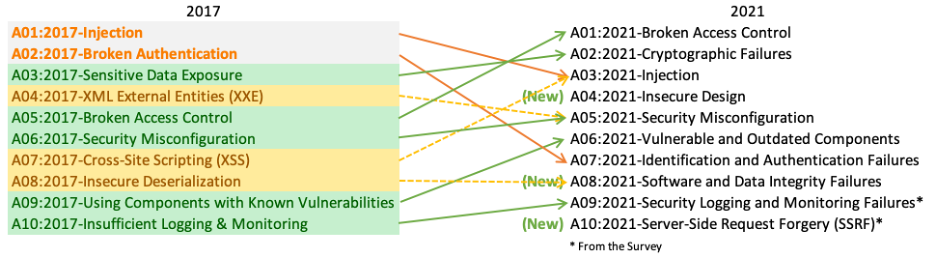
What is the OWASP Top 10 list?
The OWASP Top 10 web application security risks for 2021 are:
- Injection attacks. …
- Insecure design. …
- Security misconfigurations. …
- Vulnerable and outdated components. …
- Identification and authentication failures. …
- Software and data integrity failures. …
- Security logging and monitoring failures. …
- Server-side request forgery (SSRF).
What category is CSRF in OWASP Top 10?
CSRF is considered a flaw under the A5 category in the OWASP Top 10.
What does the OWASP Top 10 refer to?
The OWASP Top 10 is a standard awareness document for developers and web application security. It represents a broad consensus about the most critical security risks to web applications. Globally recognized by developers as the first step towards more secure coding.
Is OWASP Top 10 every 4 years?
The OWASP Top 10 is published every four years and is based on data from the previous four years. The list is not structured around how severe each vulnerability is. Instead, it compiles vulnerabilities based on how common they are so you can prevent the most common risks to sensitive data exposure.
The OWASP Top 10 is a standard awareness document for developers and web application security. It represents a broad consensus about the most critical security risks to web applications. Globally recognized by developers as the first step towards more secure coding.
For example, remote code execution, host takeover, fraud, identity theft, denial of service. The OWASP Top 10 is a popular and effective starting point for application security. It serves to give developers a quick reference of vulnerabilities they should watch …
Introduction. Welcome to the OWASP Top 10 – 2021. OWASP Top 10 Logo. Welcome to the latest installment of the OWASP Top 10! The OWASP Top 10 2021 is all-new, with a new graphic design and an available one-page infographic you can print or obtain from our home page. A huge thank you to everyone that contributed …